The most dangerous assumption in decentralized finance is that a wallet merely stores assets. In practice, the wallet is the interface through which a user interprets, authorizes, and submits instructions to software running across several blockchains. A transaction can be cryptographically valid and still be economically disastrous. That is why dApp integration, smart contract interaction, and multi-chain wallet design belong in the same conversation: each affects how clearly a user can understand the action being approved.
This distinction matters in the United States, where a typical DeFi user may move between Ethereum, layer-2 networks, and other EVM-compatible chains in a single session. The familiar workflow—connect a wallet, click “swap,” and confirm—hides a sequence of technical decisions involving chain identity, token approvals, contract permissions, gas assets, price execution, and sometimes multiple transactions. Better wallet design does not remove those risks. It makes more of them visible before the user commits.
The first myth: a wallet is a vault
A conventional wallet metaphor is useful but incomplete. In self-custodial Web3, the wallet generally does not hold a balance in the way a bank account does. Assets are recorded by smart contracts or native blockchain state, while the wallet controls keys capable of authorizing state changes. The application layer then converts a user’s intent into a transaction containing a destination, encoded function call, token amounts, fees, and other parameters.
That means signing is not the same as approving a transaction in the everyday sense. A signature proves control of a key; it does not prove that the destination is trustworthy, that the contract behaves as expected, or that the economic outcome is favorable. A malicious or poorly designed contract may use a legitimate signature to perform an action the user did not meaningfully understand.
The sharper mental model is this: a wallet is a permission boundary and an interpreter. It should help answer three questions before signing. What will this transaction call? What assets or permissions can it affect? What is likely to happen if the network executes it under current conditions? Transaction simulation is valuable because it addresses the third question, while readable decoding and approval warnings help address the first two.
How dApp integration actually works
When a decentralized application connects to a wallet, the connection usually begins with a request to identify an account and, where necessary, the active network. The dApp may then ask the wallet to sign a message, submit a transaction, or switch chains. These requests are not equivalent. A harmless-looking message can still be used in phishing workflows, while a token approval can grant a contract authority that persists beyond the immediate swap.
Smart contract interaction adds another layer of complexity because the visible interface is only a translation of an encoded function call. A button labeled “deposit” may invoke a contract method that transfers tokens and records a position. A “claim” operation may include a permit, a fee payment, or a transfer to a different address. Wallet security therefore depends partly on how well it reconstructs the underlying call in human-readable terms.
For DeFi users, the most important practical distinction is between an asset transfer and a permission grant. A transfer normally specifies an immediate movement of value. An approval can authorize a spender to move tokens later, subject to an allowance. Unlimited approvals are convenient, but they expand the consequences of a compromised contract or revoked front end. A cautious workflow treats approvals as separate security decisions rather than invisible setup steps.
Why transaction simulation helps—and where it stops
Simulation executes a proposed transaction against a representation of current or recent chain state without broadcasting it as a finalized transaction. The resulting estimate can reveal expected token changes, contract reverts, insufficient balances, and other effects. This is a major improvement over asking users to infer consequences from raw hexadecimal data or a generic confirmation dialog.
Yet simulation is not a guarantee. Its result depends on the state used for the preview and the assumptions made by the simulation environment. Blockchain state can change between simulation and inclusion. Prices can move, liquidity can disappear, a transaction can be reordered, or a contract can behave differently under conditions not captured by the preview. A simulation can also show that a transaction succeeds while the user still receives an economically poor exchange rate.
Front-running and other ordering risks illustrate the boundary clearly. If a swap has weak slippage protection, a transaction may be valid but execute at a materially worse price. A preview can identify expected outputs and warning signs, but it cannot control every event in the public transaction pipeline. Simulation is therefore best understood as a pre-flight check, not an insurance policy.
The same principle applies to smart contract audits. An audited contract may have passed a defined review, but the user may still be interacting with a counterfeit deployment, an altered front end, or a different function than intended. Security tools reduce uncertainty; they do not convert an open system into a risk-free one.
Multi-chain convenience creates a new class of mistakes
EVM compatibility makes it easier for applications and wallets to support multiple networks because many address formats and programming conventions are shared. But compatibility does not mean equivalence. The same address may refer to different contracts on different chains. A token with the same ticker can have different issuers, liquidity, decimals, or trust assumptions. Gas fees may be payable in different native assets, and bridges introduce their own contracts and failure modes.
This creates a subtle risk: users often transfer a correct asset on the wrong network. The wallet address looks familiar, the interface appears normal, and the transaction may succeed, yet the funds arrive somewhere the intended application cannot use. A multi-chain wallet should make the active chain prominent and distinguish network context from account identity. Users should also verify that the dApp supports the selected network rather than assuming that an EVM-compatible chain is automatically accepted.
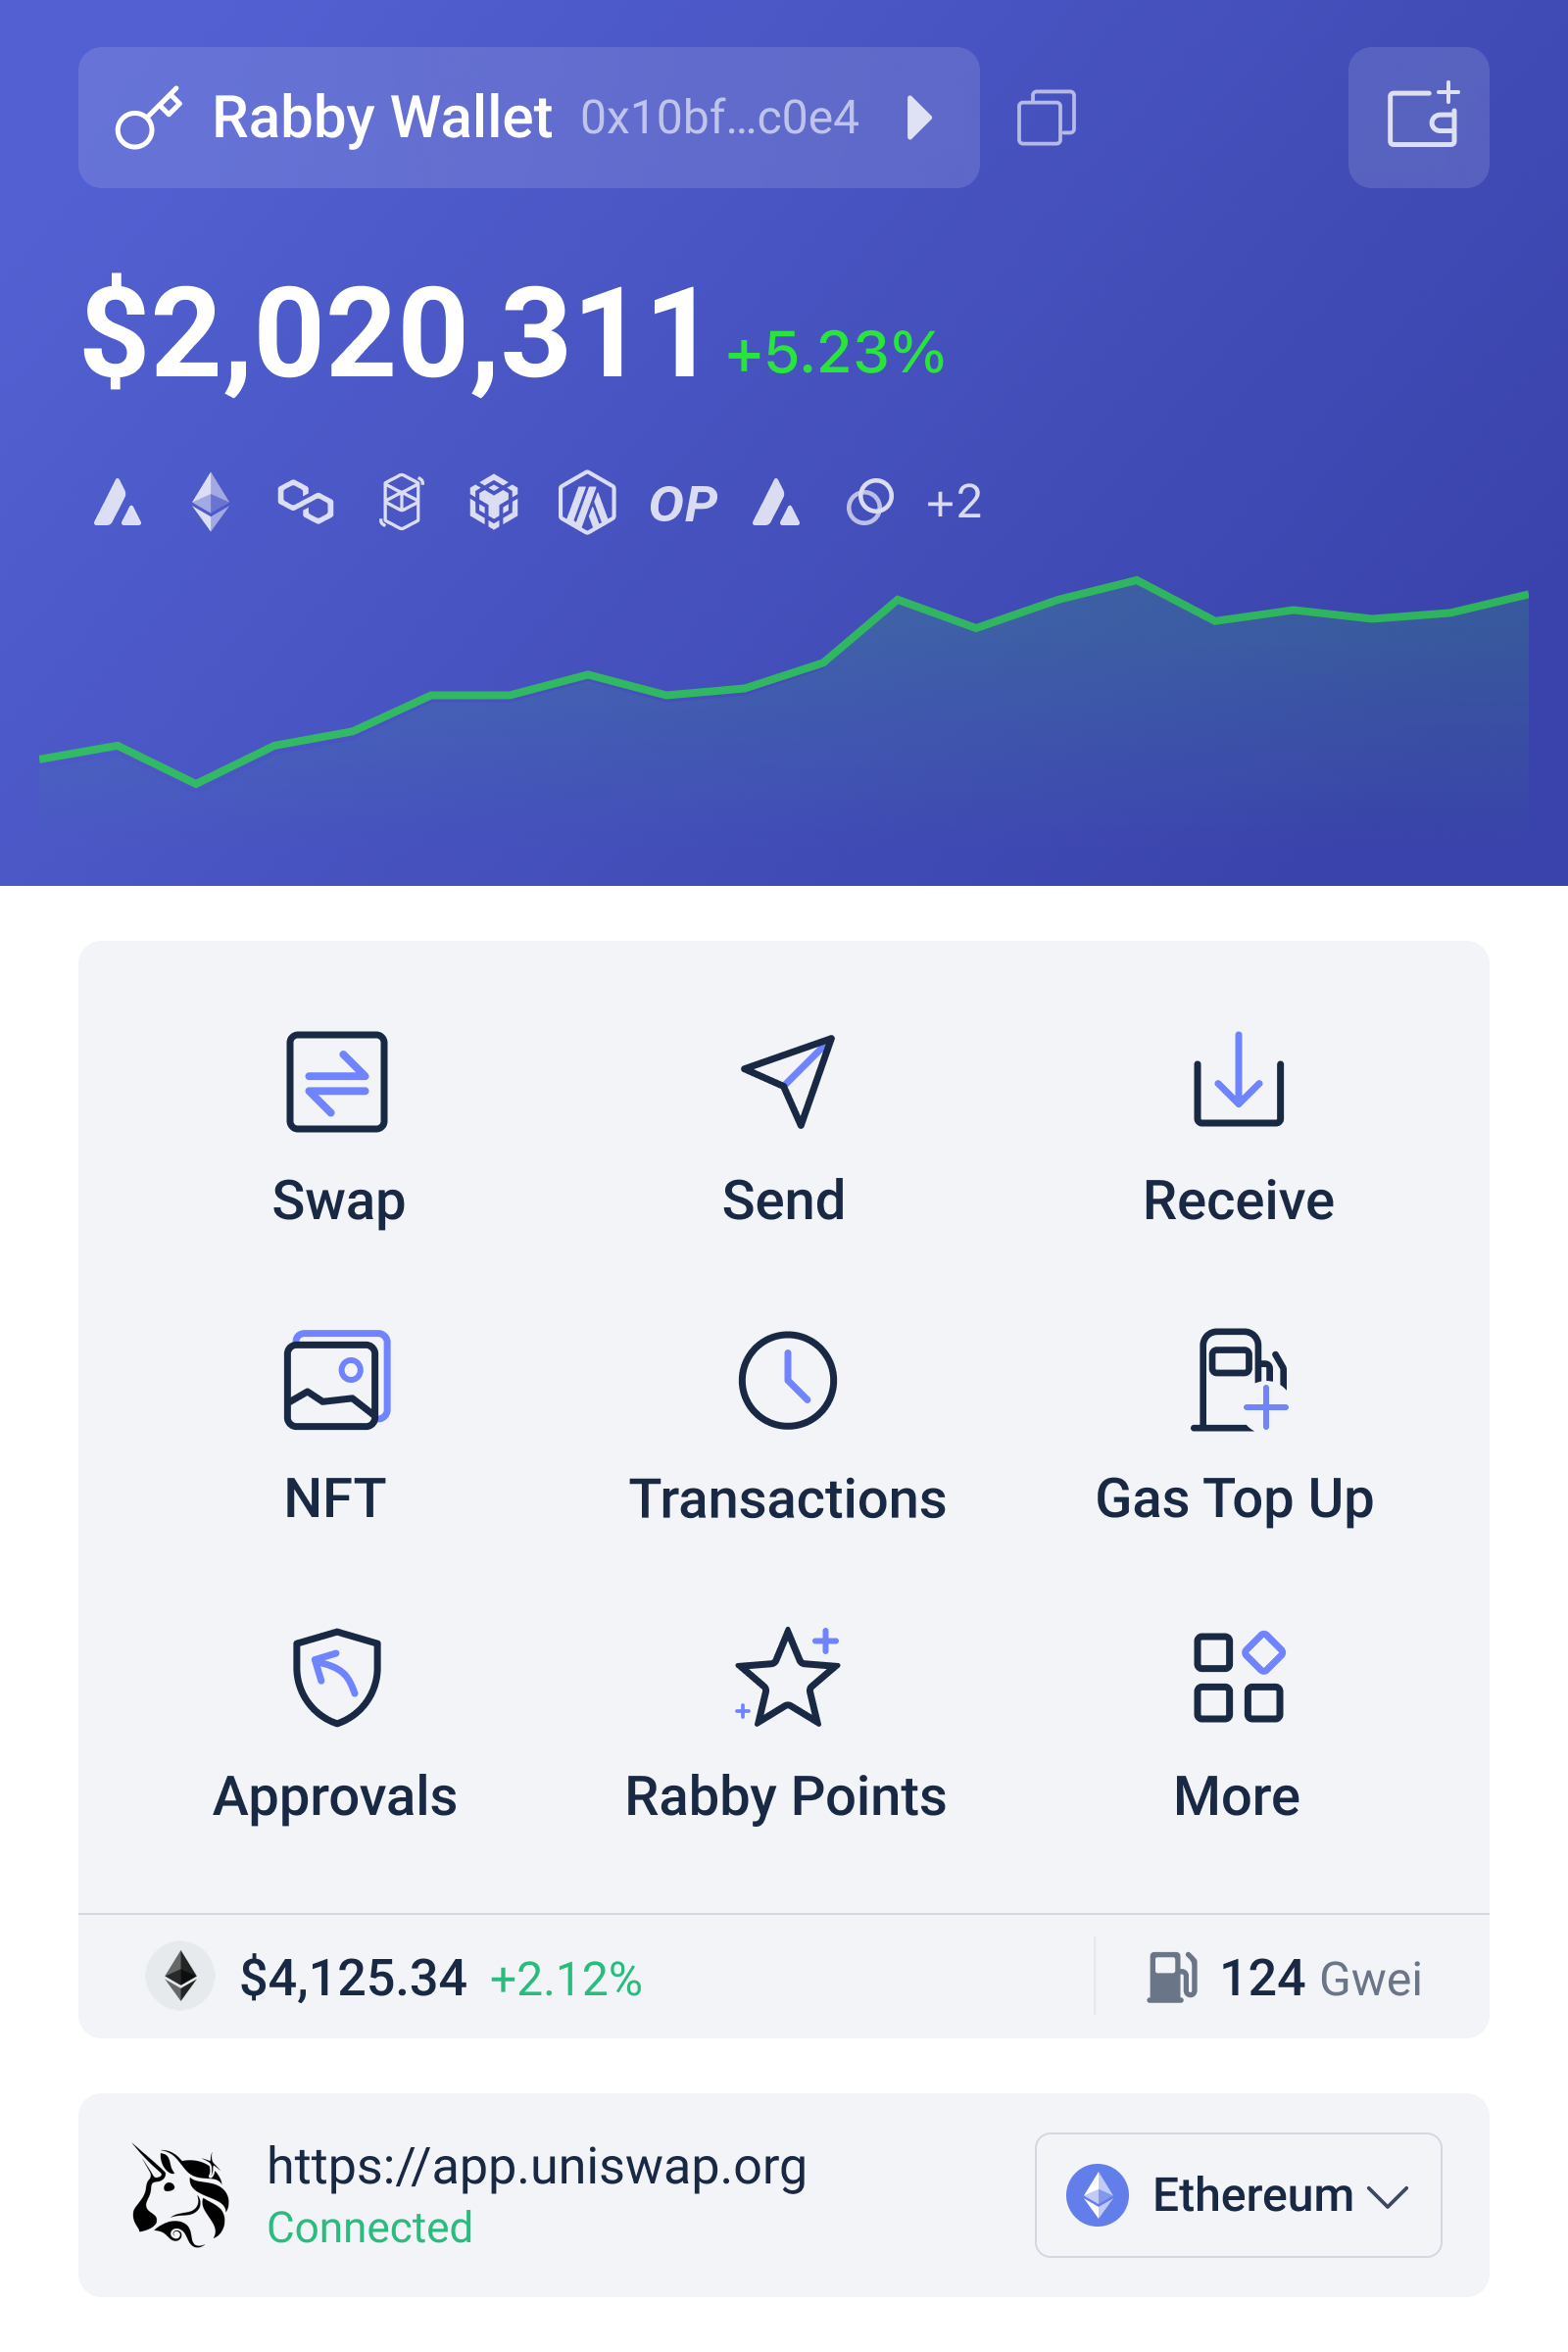
Recent positioning around wallets designed for Ethereum and EVM networks reflects a real user need: one interface can reduce the friction of switching among chains. Tools such as rabby wallet are most useful when that convenience is paired with explicit network context, transaction previews, and warnings that interrupt rather than conceal risky actions. The value is not simply supporting more chains. It is helping users compare what a proposed action means on each chain.
A practical framework for safer interaction
Before confirming a dApp transaction, a user can apply a compact four-part test. First, identify the network: is the wallet connected to the chain where the intended liquidity, collateral, or application position exists? Second, identify the authority: is the request a one-time transfer, a signature, or an allowance that may remain active? Third, inspect the outcome: which assets should leave, which should arrive, and what fees or minimum amounts apply? Fourth, assess reversibility: if the contract, front end, or price behaves badly, can the action be undone?
This framework is more reliable than judging a dApp by appearance. A polished interface can still direct users to an incorrect contract. Conversely, a technically sound protocol can present a poor confirmation experience. Security is partly a property of code and partly a property of communication between code and user.
It is also useful to separate wallet hygiene from protocol risk. Hardware-backed key storage, strong account separation, and careful approval management protect the signing authority. They do not eliminate smart contract bugs, oracle failures, bridge insolvency, liquidity shocks, or governance decisions. Users should avoid concentrating every activity in one account: a lower-value testing account can limit the consequences of an unfamiliar interaction, while a long-term holdings account can remain disconnected from experimental applications.
What to watch as wallet design evolves
The next meaningful improvement is unlikely to be a single warning banner. It will be better context: clearer contract identity, stronger comparison of before-and-after balances, more precise approval controls, and simulations that explain not only whether a transaction succeeds but why its result matters. If multi-chain activity continues to expand, wallets may increasingly function as risk dashboards rather than passive signing windows.
That development would create a new trade-off. More warnings can improve safety, but excessive alerts produce habituation; users eventually approve everything to make the interface disappear. Effective security design must therefore prioritize warnings by severity and explain the mechanism behind them. A message such as “unusual approval scope” is more useful when it tells the user what the spender can do, for how long, and which token balance is exposed.
The enduring lesson is simple but easily missed: convenience and safety are not opposites, yet convenience without interpretation is fragile. A multi-chain wallet earns its value by reducing the gap between what a dApp displays and what the blockchain will actually execute. Users still need judgment, especially around approvals, bridges, unfamiliar contracts, and changing market conditions. But a wallet that simulates transactions and explains permissions can move that judgment earlier—before an irreversible signature becomes a costly lesson.
Frequently Asked Questions
Does transaction simulation guarantee that a DeFi transaction is safe?
No. Simulation can reveal likely state changes, reverts, and suspicious outcomes, but it relies on a particular view of blockchain state. Prices, liquidity, transaction ordering, and contract conditions may change before execution. Treat simulation as an important pre-flight check, not a guarantee.
Why can the same wallet address create confusion across chains?
EVM networks often use compatible address formats, but each network has separate state and deployments. The same address may hold different assets on different chains, and a contract at a familiar-looking address may not be the intended contract on another network. Always verify the active chain and the application’s supported network.
Are token approvals more dangerous than ordinary transfers?
They can be, because an approval may grant a contract permission to move tokens after the original transaction. The risk depends on the approved amount, the spender, and whether the allowance remains active. Review approval scope and revoke allowances that are no longer necessary, particularly after using unfamiliar applications.